Make every transfer event attributable
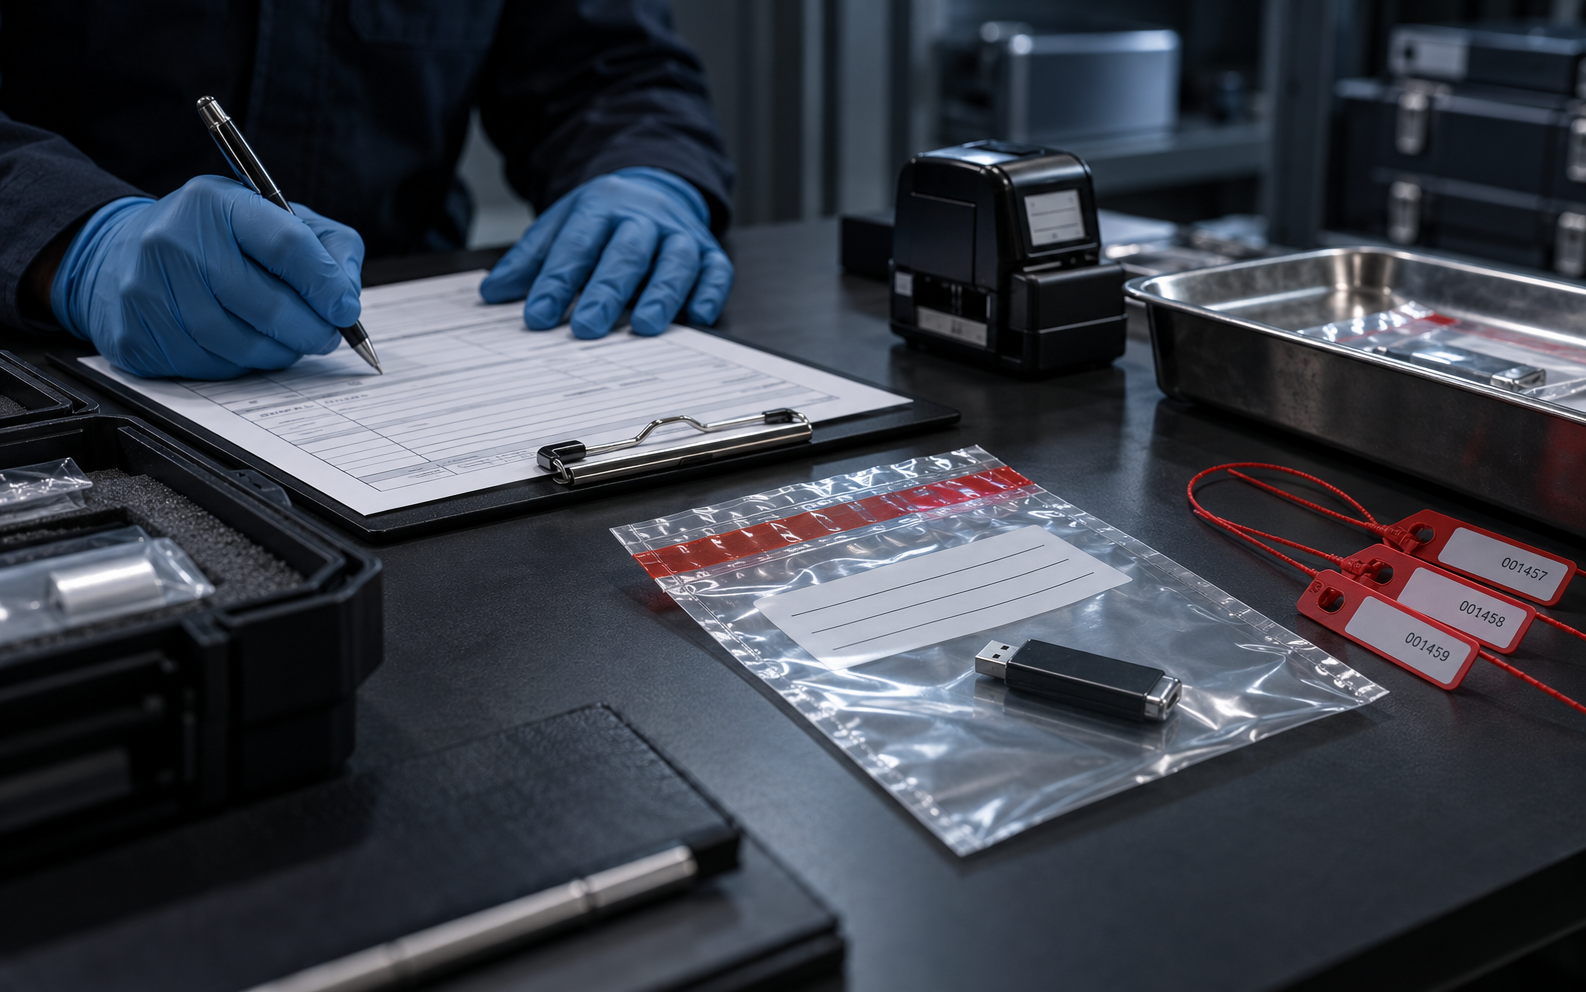
Chain of custody is an operational record: who controlled the device, what package it carried, when custody changed and whether seals or integrity checks matched. It is not improved by copying the confidential evidence into the log.
The coordinator seals the drive, records the seal and package manifest, transfers it to a courier and obtains recipient acknowledgment. The auditor records opening time, seal condition, device identity and integrity result.
Run the control in five steps
- 01Assign a unique handoff and device identifier.
- 02Record package manifest and integrity values before sealing.
- 03Capture every sender, carrier, recipient, time and condition.
- 04Require recipient acknowledgment and discrepancy reporting.
- 05Close custody only after return, retention or approved disposal.
Preserve an accountable audit trail
Keep handoff ID, request, device serial, seal ID, manifest version, hash method, sender, carrier, recipient, timestamps, condition, exceptions and final disposition.
Stop and investigate when
- A custody interval has no accountable person.
- Seal or device identifier differs at receipt.
- The log contains passwords or copied evidence.
State what the control does not prove
Do not equate with hardware-encrypted drives or untested Mac/Android compatibility. Validate the device, recipient environment, secret channel, plaintext residue and recovery workflow separately.
Audit handoff questions
Does a courier receipt replace chain of custody?
No. It proves shipment, not package scope, device identity, seal condition or recipient validation.
Should the password be in the custody log?
No. Record the channel and authorized sender, not the secret.
Sources for this decision
Links support specific control decisions and do not imply endorsement.